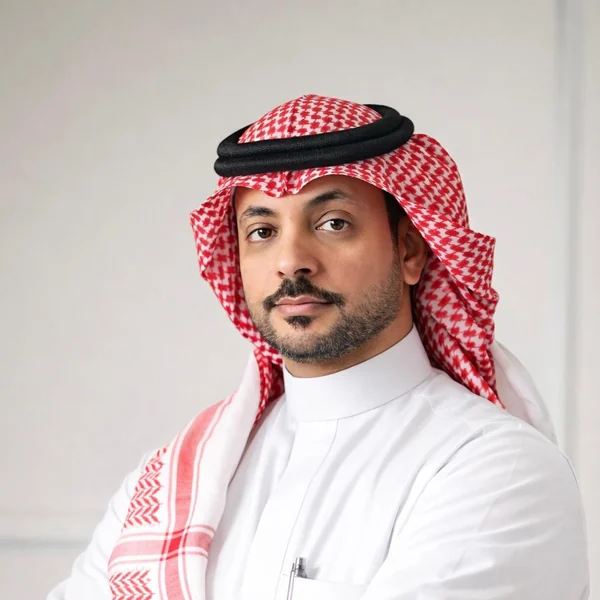
Naif Alshahrani
Cybersecurity GRC Director
Naif Alshahrani is Cybersecurity GRC Director at an organisation whose name the organiser does not disclose. Governance, risk and compliance is the discipline that turns written controls into something measurable inside an organisation: setting policy and risk matrices, assigning risk owners, measuring maturity, running internal and external audit cycles, and demonstrating compliance to regulators. In industrial settings it is harder still, because legacy control systems cannot tolerate ordinary scanning tools, so compensating controls and documented risk acceptance take the place of off-the-shelf solutions.